

How impersonation works
When a user is impersonated:- The impersonator sees Lightdash exactly as that user sees it, including their permissions, spaces, and data access.
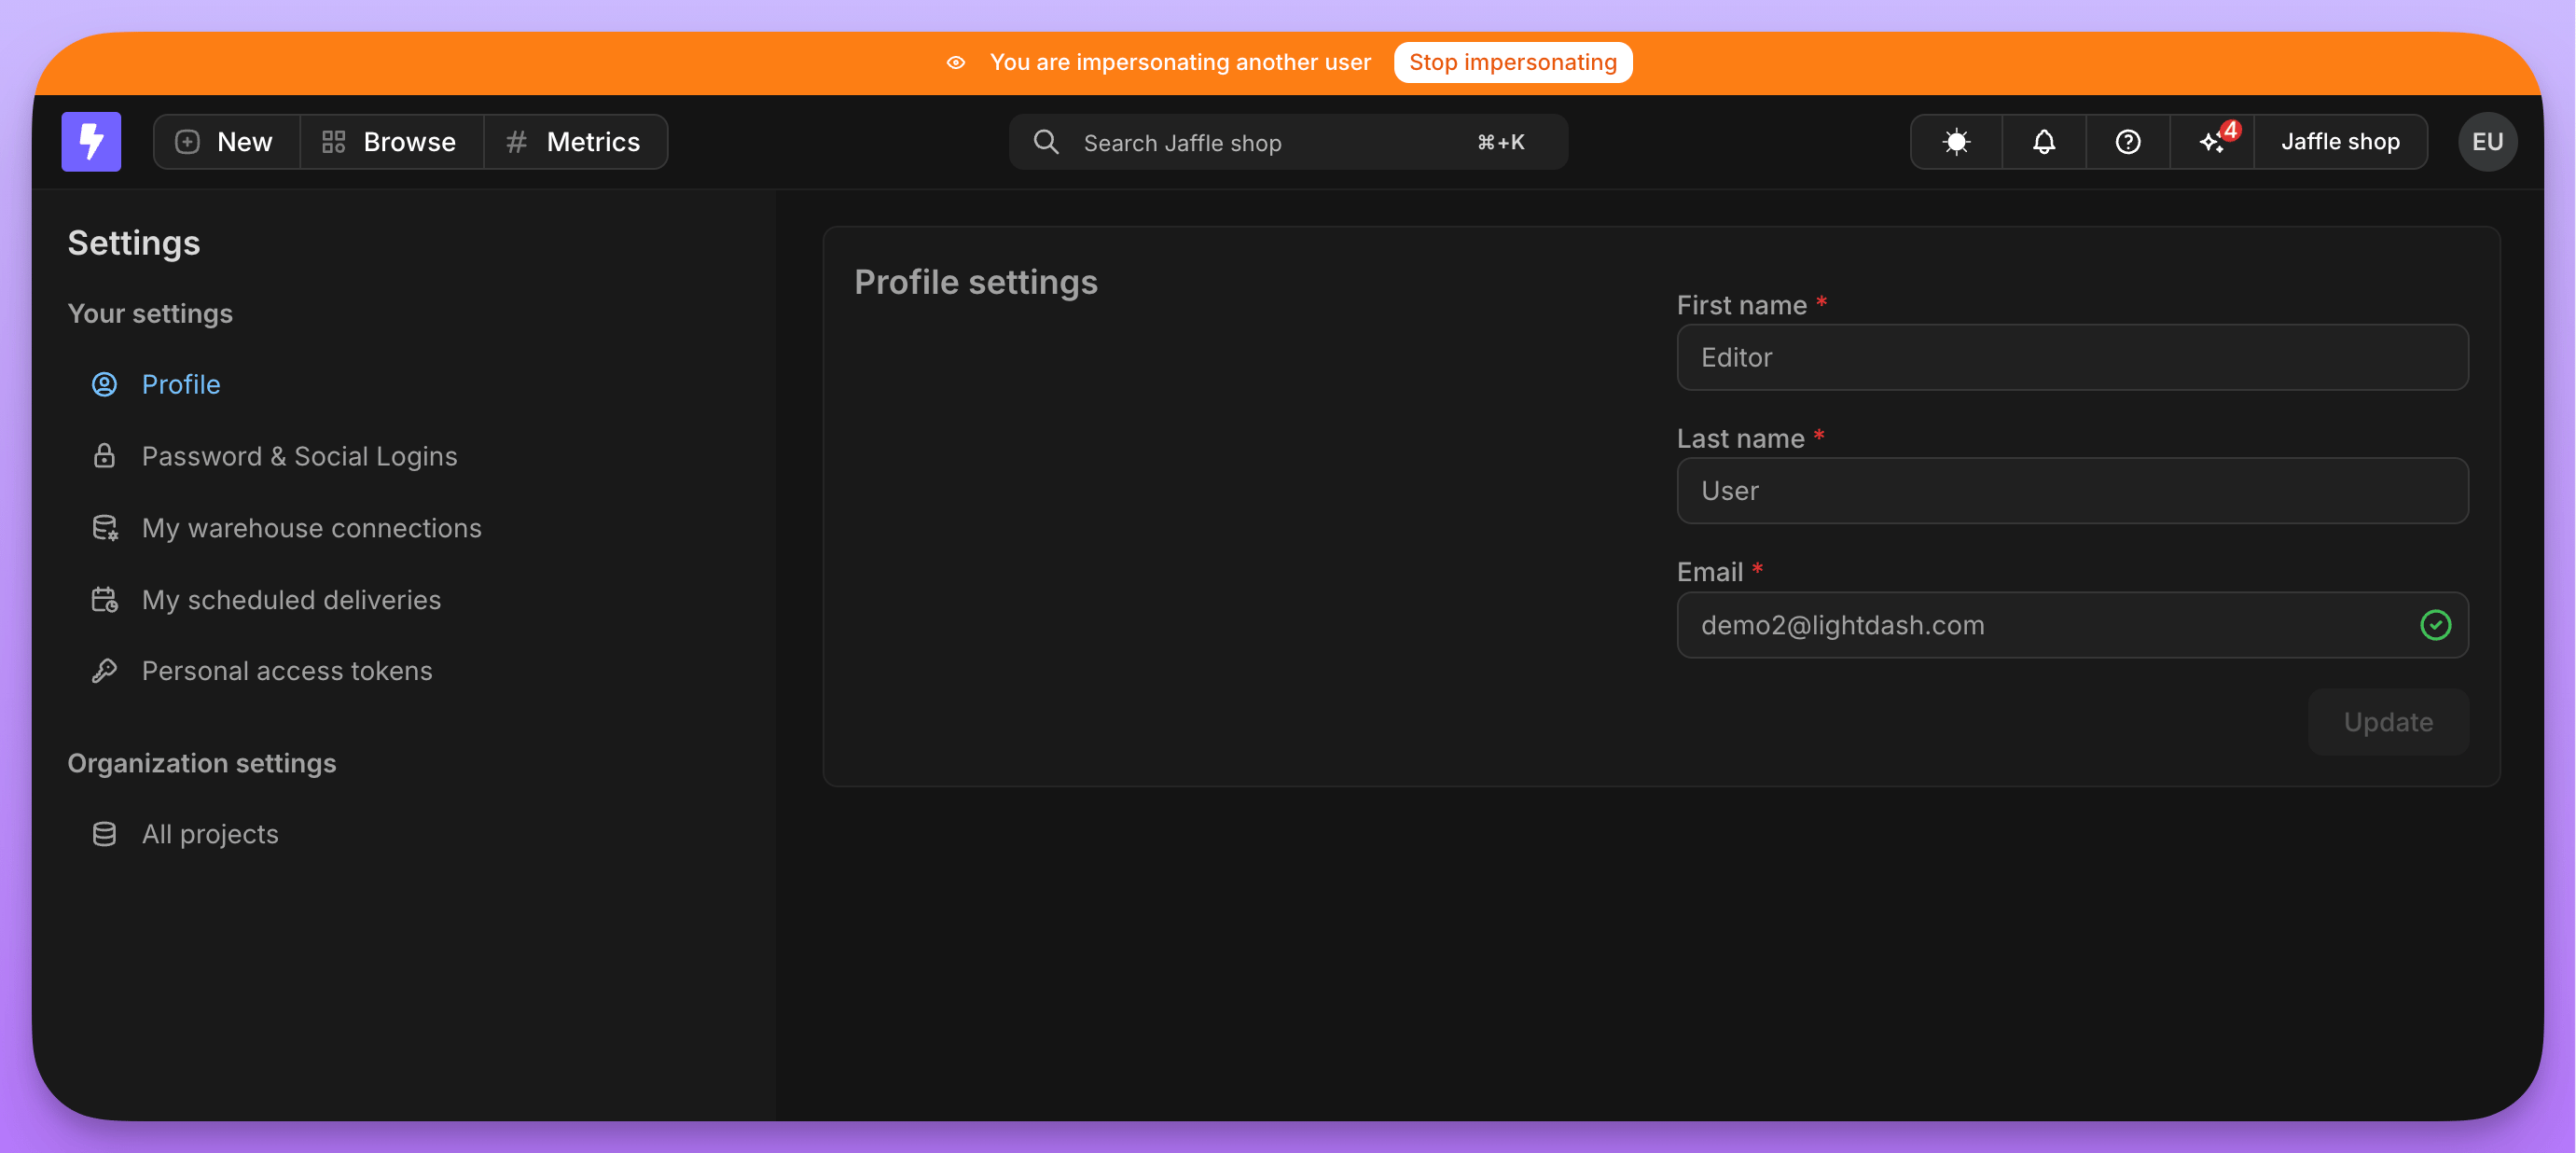
- A banner appears at the top of the screen indicating an impersonation session is active.
- Each session has a hard limit of 15 minutes, after which it ends automatically.
- The impersonator can stop at any time from the banner.
userUuid and the impersonated user’s userUuid.
If the project requires users to provide their own personal warehouse credentials, queries run with the impersonated user’s credentials, including SSO-backed credentials.
Impersonation by your admins
Impersonation by organization admins is behind a feature flag. On Lightdash Cloud, contact support to enable it for your organization. Self-hosted instances enable it themselves, as described below.
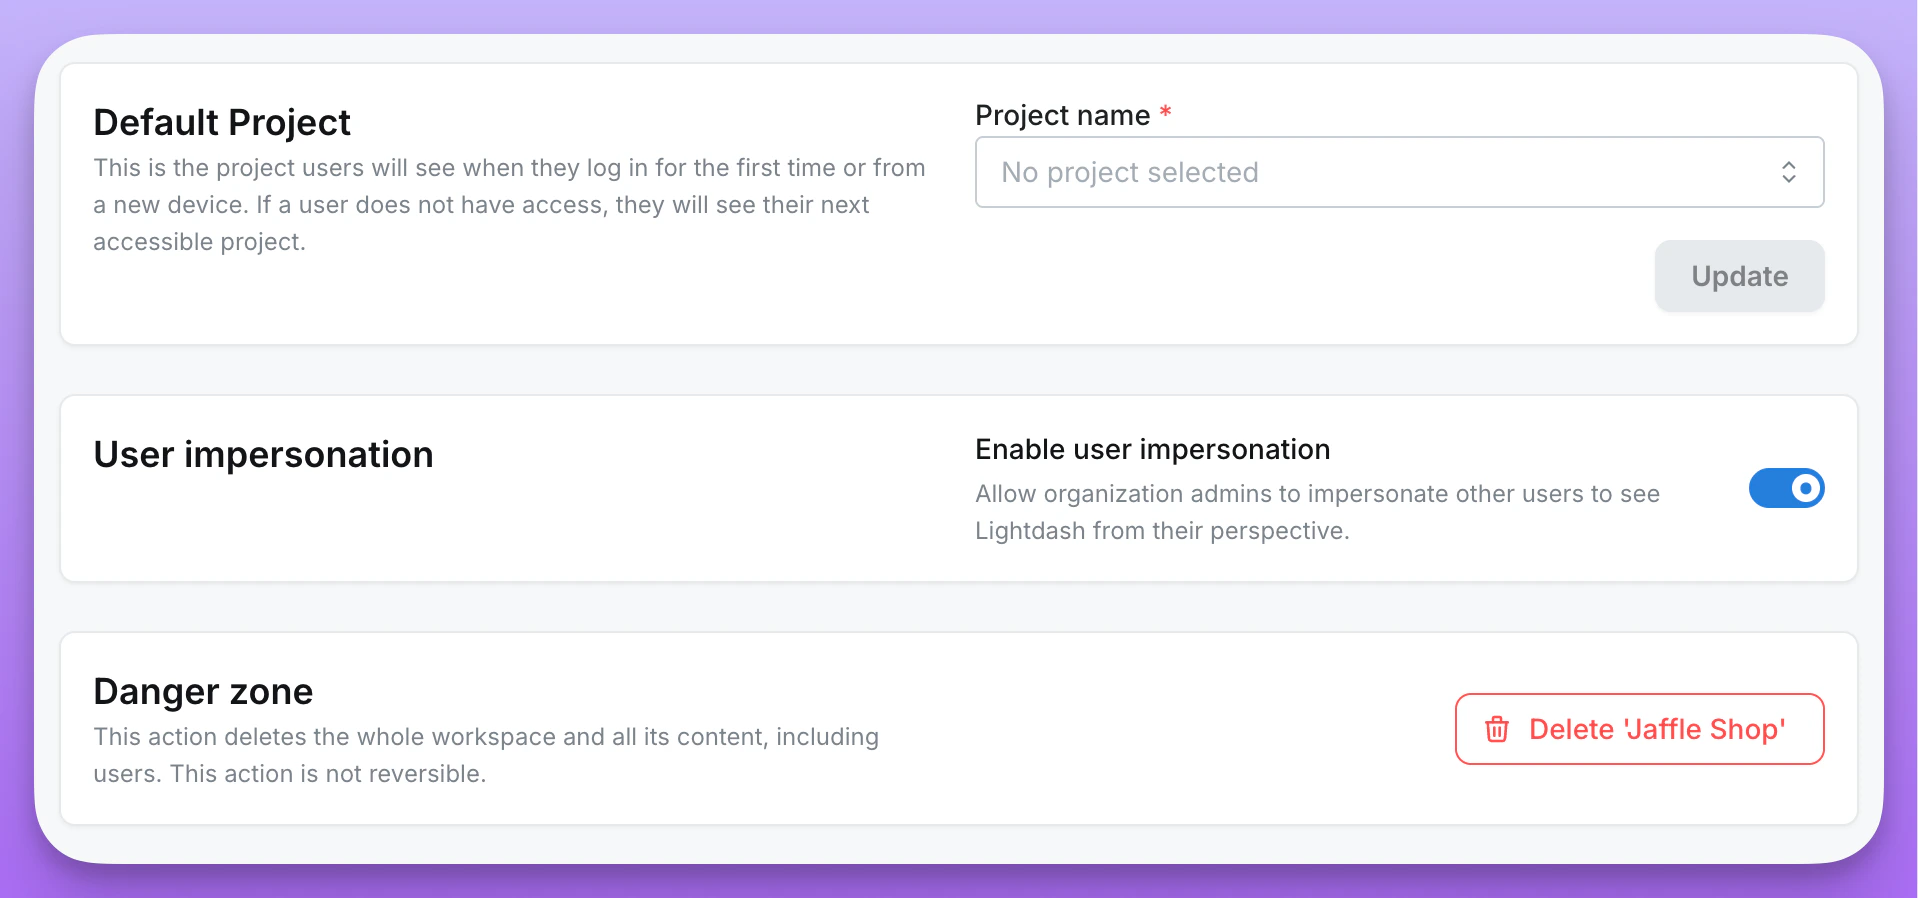
impersonate:User scope, together with manage:OrganizationMemberProfile so the user can open Users & groups to pick someone. Once the feature is available, an organization admin goes to Settings → General (under Organization settings) and turns on Enable user impersonation in the User impersonation section. Turn it off there at any time.
Self-hosted instances turn on the feature flag themselves:
- Add
user-impersonationto theLIGHTDASH_ENABLE_FEATURE_FLAGSenvironment variable. The value is a comma-separated list of flag IDs, so if you already set it, append the ID, for exampleLIGHTDASH_ENABLE_FEATURE_FLAGS=embedding,user-impersonation. See feature flags. - Restart Lightdash so the new value takes effect.
Starting a session
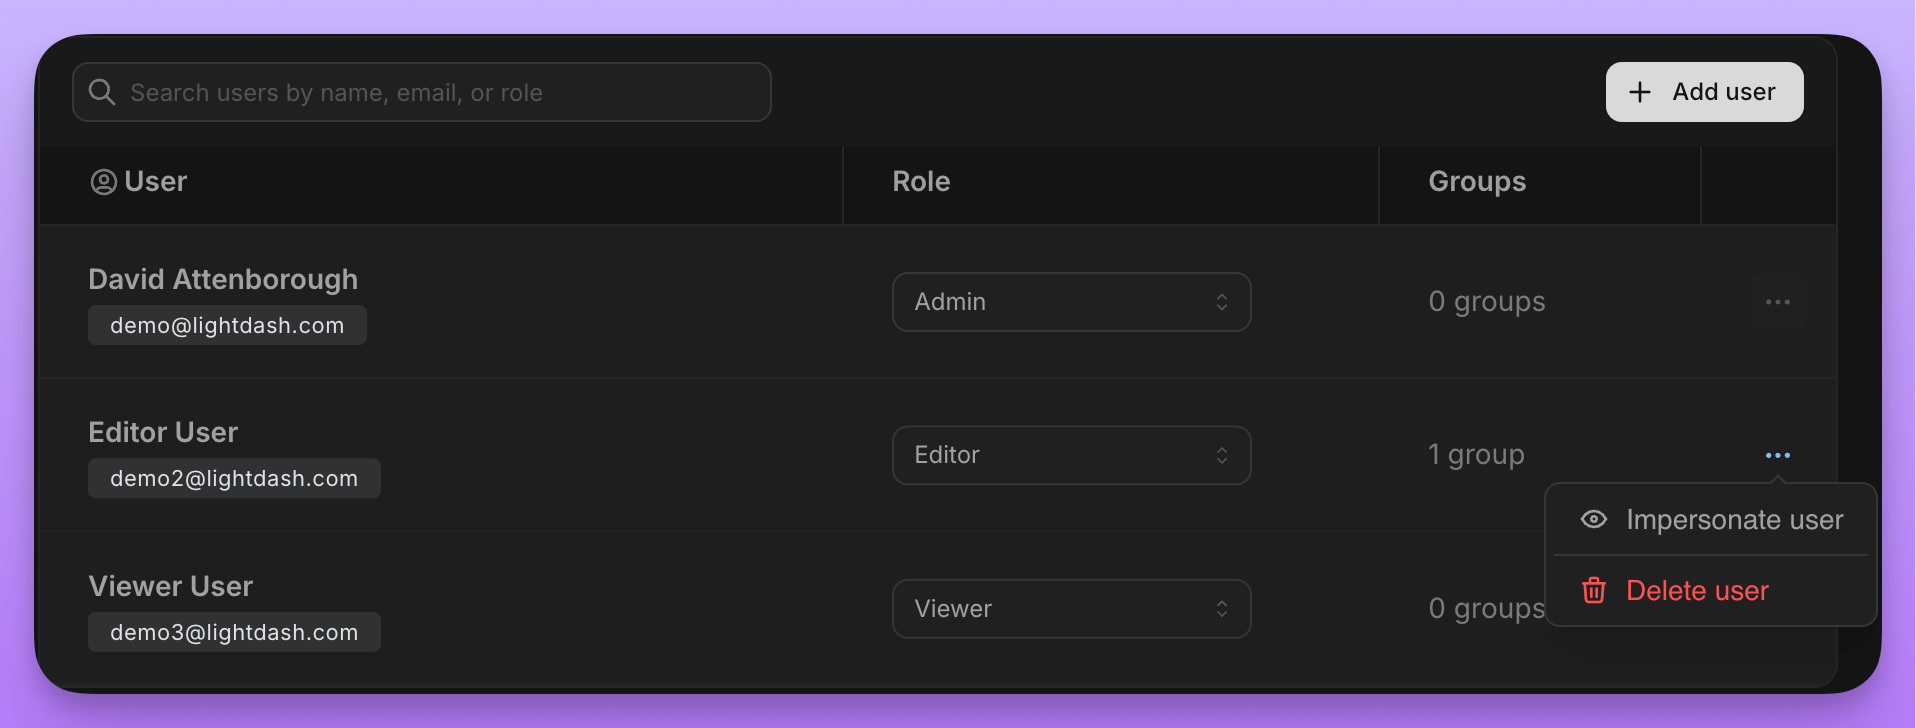
You can only impersonate a user who has accepted their invite and signed in at least once. For a pending user, the … menu shows Send new invite (or Get new link) instead of Impersonate user.- Go to Settings → Users & groups (User management when groups aren’t enabled).
- Find the user you want to impersonate.
- Click the … menu next to their name.
- Select Impersonate user.
Stopping a session
Click Stop impersonating in the banner to return to your normal admin view.Impersonation by the Lightdash support team
Lightdash support access is an organization-wide consent toggle, off by default. Until an admin opts in, the support team cannot impersonate anyone in your organization. Turn it on when you have an open support ticket and need the team to reproduce a user-specific issue without granting consent each time they investigate. Turn it off once the issue is resolved. When it is on, support impersonation follows the same mechanics described above. Only organization admins can change the setting.Enabling support access
- Go to Settings → General.
- Find the Lightdash support access card.
- Switch Allow Lightdash support to impersonate users on.